Bank AML and KYC Training Requirements: Frequency, Curriculum, and Audit Evidence
Commercial banks and depository financial institutions operate under extraordinary regulatory scrutiny across all operational tiers. Specifically, global money laundering schemes, terrorist financing networks, and evasive sanctions violations present an existential threat to the integrity of the international financial ecosystem. Consequently, federal enforcement agencies impose stringent mandates on financial institutions to maintain robust, verified compliance programs. These supervisory authorities include the Financial Crimes Enforcement Network (FinCEN), the Federal Deposit Insurance Corporation (FDIC), the Federal Reserve, and the Office of the Comptroller of the Currency (OCC). Ultimately, at the operational center of every regulatory examination sits human capital.
While transaction monitoring systems and machine learning algorithms flag statistical anomalies, trained professionals must analyze, escalate, and prevent illicit financial flows. Therefore, when financial institutions fail to maintain comprehensive aml training requirements, regulatory authorities issue devastating enforcement actions. Furthermore, severe civil money penalties and public consent orders disrupt operational viability and destroy shareholder value. Managing regulatory qualifications across diverse banking departments requires specialized technological infrastructure. Financial leaders can benchmark leading platforms by exploring our guide on the
best training management software available today.
A compliant anti-money laundering and know-your-customer framework cannot function as a generic, annual administrative exercise. Instead, supervisory examiners actively test whether banking staff understand the practical compliance risks associated with their exact job functions. Unfortunately, off-the-shelf training modules routinely fail regulatory audits because they lack contextual relevance to the specific risk assessment of the institution. For example, a frontline teller requires fundamentally different operational awareness than a commercial loan officer or a wire room operator. Therefore, institutions must establish a role-tailored curriculum backed by tamper-proof documentation. Exploring our guide on an
LMS for compliance training and audit evidence illustrates how modern platforms satisfy strict regulatory examiners.
Key Takeaways
Statutory Mandate:
Ongoing employee training is one of the foundational core pillars of a compliant Bank Secrecy Act and Anti-Money Laundering program required under federal banking regulations.
Risk-Commensurate Frequency:
While annual refreshers provide a basic baseline, high-risk departments, new hires, and personnel in high-velocity transaction corridors require more frequent, event-driven educational cycles.
Role-Specific Curriculum:
Examiners strictly penalize generic training programs; course materials must be meticulously tailored to the distinct operational risks faced by branch tellers, commercial onboarding officers, wire specialists, analysts, and board directors.
Comprehensive Audit Evidence:
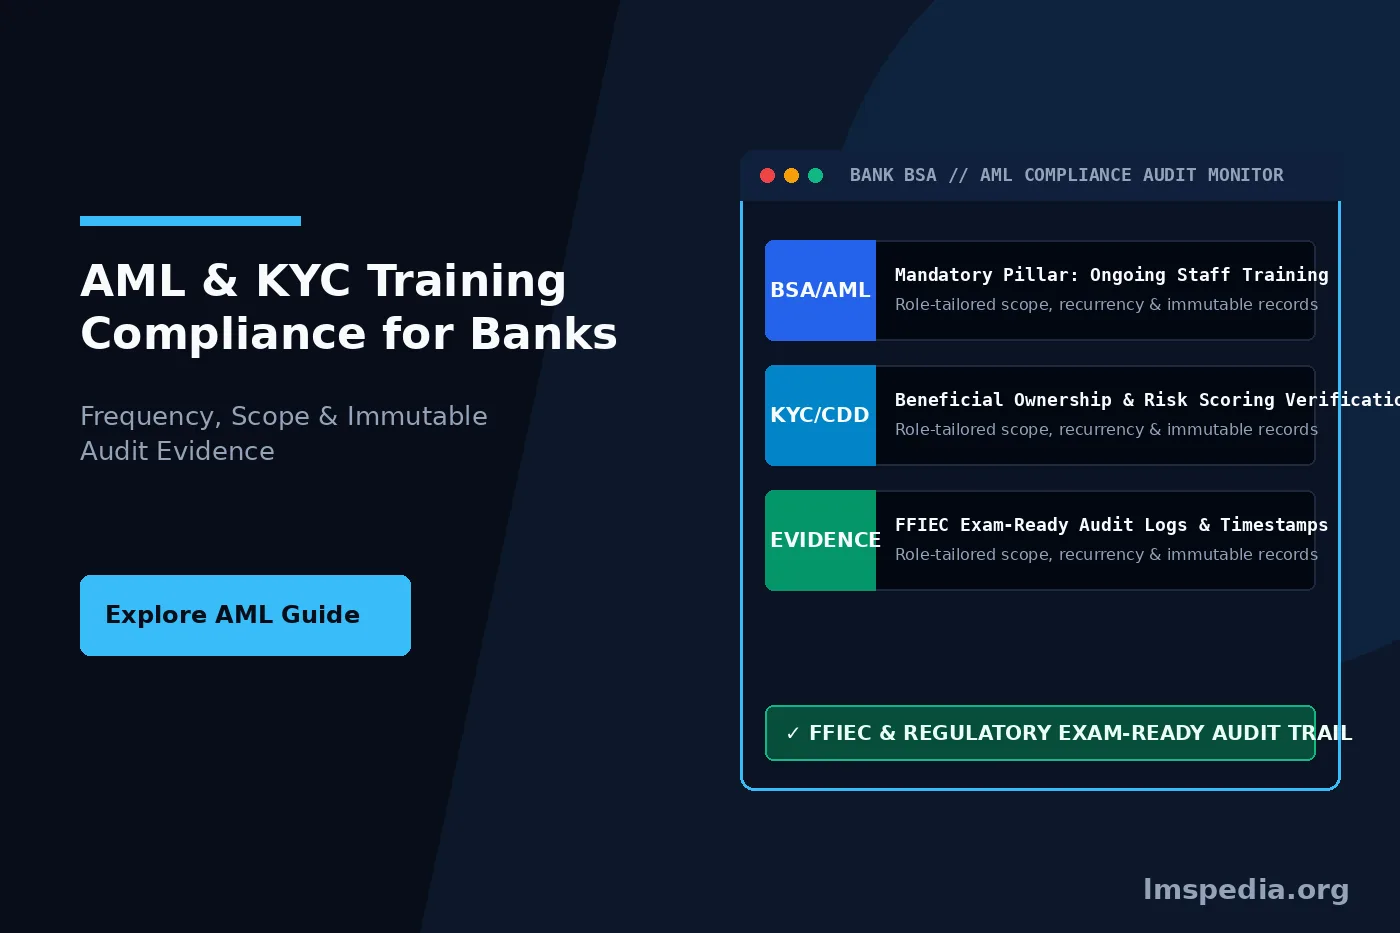
Financial institutions must maintain detailed, immutable records for a minimum of five years, including course syllabi, attendee timestamps, passing test scores, and executive escalation logs for delinquent learners.
Board Governance:
Bank boards of directors hold ultimate legal accountability for compliance health, requiring specialized governance training and regular reporting documented within official board minutes.
The Regulatory Framework Governing Bank AML and KYC Training
The legal foundation of financial crime education in the United States originates within the Bank Secrecy Act (BSA) of 1970. Subsequently, the USA PATRIOT Act of 2001 and the Anti-Money Laundering Act of 2020 bolstered statutory oversight significantly. Under regulatory pillars codified across federal banking statutes, every insured depository institution must establish and maintain a written BSA compliance program. The official regulatory text is accessible through the
Electronic Code of Federal Regulations portal.
Furthermore, federal regulations explicitly establish core operational pillars for depository institutions. Alongside internal controls, an independent compliance officer, independent audit testing, and customer due diligence, ongoing employee training stands as an unyielding legal mandate. Regulatory authorities do not treat staff education as an optional administrative recommendation. The
Federal Financial Institutions Examination Council establishes strict supervisory expectations across all federal banking agencies. Specifically, failing to train appropriate personnel triggers a direct deficiency citation in the overall compliance program.
Consequently, training failures trigger formal supervisory rating downgrades under the Uniform Financial Institutions Rating System. Examiners evaluate whether training initiatives reflect updates to statutory reporting thresholds and newly emerged money laundering typologies. Moreover, curriculums must incorporate expanding sanctions programs enforced by the
Office of Foreign Assets Control. Therefore, financial institutions must maintain agile learning pipelines capable of deploying immediate curriculum updates when international sanctions lists expand.
Regulatory Alignment Strategy
Never separate your training curriculum design from your annual institutional risk assessment; if your bank expanded correspondent banking or commercial real estate portfolios, your syllabus must explicitly address those high-risk categories to satisfy FFIEC examiners.
Determining Anti Money Laundering Training Frequency
Depository institutions frequently struggle with the operational definition of educational cadence. Specifically, the Bank Secrecy Act mandates that compliance education must be ongoing, yet federal statutes avoid setting a rigid calendar schedule. Consequently, this statutory flexibility leads some compliance teams to mistakenly believe that a single annual multiple-choice refresher satisfies all legal obligations. In reality, supervisory examiners evaluate anti money laundering training frequency through the lens of institutional risk, employee turnover, and operational exposure.
While an annual baseline refresher represents the absolute minimum acceptable standard for general staff, high-risk operational units demand increased frequency. For example, frontline branch personnel, compliance analysts, and foreign wire transfer teams require quarterly or bi-annual educational touchpoints. Ultimately, frequent instruction helps staff stay ahead of sophisticated criminal schemes. Frequency schedules must also account for sudden geopolitical events that trigger emergency sanctions revisions. Relying strictly on a single annual event leaves the institution highly vulnerable to compliance lapses during intervening operating quarters.
In addition to scheduled calendar intervals, event-driven training triggers must be formalized within bank compliance policy. Specifically, new personnel must complete foundational AML and KYC coursework immediately upon hire. Frontline employees must never obtain authorization to process live transactions or open customer accounts prior to completing certified compliance onboarding. Furthermore, when an employee transitions to a new department, the internal transfer should automatically trigger targeted, role-specific coursework. System administrators can diagnose institutional training intervals across varied business units by utilizing
training needs assessment tools to map departmental skill deficiencies accurately.
Role-Based Curriculum Scope: Tailoring KYC Training Compliance
A primary deficiency identified during regulatory examinations is the distribution of generic training materials across disparate departments. Instead, regulators demand that institutions tailor their kyc training compliance and AML curricula to the distinct risks encountered by specific operational roles. Tailored training ensures that personnel understand exactly how financial crimes manifest within their daily workflows. Below, we examine the mandatory curriculum scopes required across primary banking functions.
Frontline Tellers and Branch Customer Service Staff
Frontline branch personnel serve as the primary defensive barrier against illicit physical cash placement. Therefore, branch training must focus heavily on recognizing behavioral indicators associated with currency structuring, commonly known as smurfing. Specifically, structuring occurs when bad actors break large cash amounts into smaller transactions below the ten-thousand-dollar threshold to evade Currency Transaction Reports. Furthermore, tellers must learn to identify fraudulent identification cards, manage suspicious walk-in customers requesting sequential cashier checks, and escalate suspicious interactions discreetly. Frontline staff must master internal escalation protocols without alerting the customer, as tipping off a suspect constitutes a severe federal crime.
Account Opening Personnel and Commercial Onboarding Officers
Employees responsible for customer onboarding must master the Customer Identification Program and Customer Due Diligence rules under FinCEN regulations. Specifically, training must guide staff through identifying the true Ultimate Beneficial Owners of complex legal entities, including multi-layered limited liability companies, offshore trusts, and foreign holding structures. Additionally, onboarding officers must learn how to establish accurate customer risk profiles and gather documentary verification systematically. Staff must identify high-risk classifications, such as Politically Exposed Persons, foreign non-governmental organizations, and cash-intensive businesses, which require mandatory Enhanced Due Diligence protocols.
Wire Operations, Payments, and Trade Finance Specialists
Back-office payment processing teams operate within high-velocity, high-value transaction corridors daily. Consequently, curriculum for wire transfer personnel must emphasize real-time sanctions screening and rapid transaction monitoring alert disposition. Specialists must learn to identify complex payment anomalies, including stripping originating customer data from payment messages. In addition, trade finance teams require advanced instruction demystifying trade-based money laundering schemes. Training modules must cover over-invoicing, under-invoicing, phantom shipments, and dual-use goods verification to prevent illicit capital movement through global commercial supply chains.
Dedicated BSA and AML Compliance Analysts
Specialized compliance personnel responsible for monitoring transaction queues and filing Suspicious Activity Reports require comprehensive technical education. Specifically, training for analysts must cover advanced financial forensic techniques, law enforcement liaison protocols, and information-sharing mechanisms under Sections 314(a) and 314(b) of the USA PATRIOT Act. Furthermore, analysts must master clear, defensible narrative drafting techniques. A poorly written narrative delays law enforcement investigations and routinely invites severe regulatory criticism during supervisory compliance examinations.
Executive Management and the Board of Directors
The board of directors holds ultimate legal governance responsibility for the operational compliance program of the financial institution. However, directors do not require transactional training on completing routine administrative forms. Instead, executive education must center on corporate governance, risk appetite, resource allocation, and personal fiduciary liability. Ultimately, directors must understand the institutional consequences of program deficiencies, the severe financial impact of civil money penalties, and their statutory obligation to maintain an adequately funded compliance infrastructure.
Building a Unified Financial Crime Training Architecture
Modern money laundering schemes rarely operate in complete isolation from external cyber threats. For instance, organized criminal syndicates routinely combine cyber fraud, synthetic identity theft, and commercial entity manipulation to funnel illicit capital through the commercial banking sector. Consequently, forward-thinking institutions organize their educational efforts under a unified financial crime training program that merges AML, KYC, sanctions screening, and anti-fraud curricula.
When internal fraud prevention and anti-money laundering disciplines remain separated in operational silos, institutional blind spots emerge rapidly. For instance, an unauthorized account takeover might appear to the fraud department as an isolated retail dispute, whereas the compliance team would recognize the subsequent rapid international wire transfer as an integration stage of money laundering. Therefore, structuring your curriculum around integrated financial crime scenarios helps employees connect transactional anomalies to broader illicit networks. Training directors can evaluate pedagogical strategies to ensure theoretical instruction produces measurable behavioral change by reviewing our guide on
transfer of training.
Exam Survival Strategy
During a regulatory exam, never provide unorganized spreadsheet exports of training logs; prepare a pre-indexed audit package containing your approved training policy, the syllabus mapped to your risk assessment, role-specific attendance sheets, and verified test scores.
Benchmarking Banking Compliance Platforms
Administering enterprise-scale compliance education across thousands of bank employees, contractors, and corporate directors requires specialized learning operations software. Specifically, the software platform must maintain absolute data integrity, granular audit trails, and multi-tiered scheduling capabilities. Below, we compare leading software solutions based on their financial compliance tracking capabilities.
| Platform / Solution |
Primary Focus |
Compliance & Training Administration Strength |
| SimpliTrain |
End-to-end commercial training operations, resource logistics, and automated credential scheduling. |
Streamlines administrative coordination, tracks enterprise certifications, and automates multi-department compliance schedules with immutable audit logging for regulatory examinations. |
| Thomson Reuters Compliance Learning |
Regulatory content library and global compliance tracking. |
Offers deeply researched, pre-built financial services compliance courses with direct regulatory updates, but features limited native capabilities for managing offline classroom logistics. |
| SAI360 |
Integrated governance, risk, and compliance management. |
Combines policy management, risk assessment tracking, and enterprise regulatory training delivery across broad corporate environments. |
Selecting the correct technical architecture ensures your compliance data remains secure, auditable, and easily accessible during unannounced regulatory examinations. Furthermore, connecting learning management infrastructure with core banking directories requires strict administrative governance. To configure your administrative permissions properly and avoid unauthorized visibility into sensitive personnel files, review our technical breakdown on how to architect
secure LMS user roles and permissions.
Audit Evidence and BSA Training Records: What Examiners Demand
In regulatory banking supervision, an unwritten legal maxim governs all examinations: unrecorded training legally never occurred. For example, an institution might deliver an exceptional anti-money laundering lecture, but if the training records are incomplete, examiners will issue formal supervisory citations. Therefore, establishing meticulous bsa training records represents an indispensable requirement of safe and sound banking operations.
When regulatory examiners utilize the FFIEC BSA/AML Examination Manual to evaluate an institution, they issue a formal Request for Information covering training documentation. Consequently, compliance officers must produce specific, verifiable artifacts covering the entire examination period, which typically spans twelve to twenty-four months. The essential regulatory audit evidence package must include five core elements:
-
Comprehensive Course Syllabi and Materials: Examiners demand copies of all training modules, presentation decks, handouts, and video transcripts utilized during the supervisory cycle. Regulators review the content to verify that the curriculum covers mandatory statutory provisions and red flags specific to the bank’s geographic markets.
-
Detailed Attendance and Completion Logs: Records must capture the full legal name of each employee, unique identifier, official job title, department, date of course completion, and system timestamps. Physical or verified digital sign-in sheets are strictly required for instructor-led classroom sessions.
-
Comprehension Verification and Assessment Scores: Merely recording seat time or digital page-turning is entirely insufficient. Instead, regulators expect measurable verification of comprehension, requiring platforms to store passing quiz scores, track retake attempts, and document remedial training administered to personnel who failed initial testing.
-
Tracking of Delinquent Learners and Escalation Logs: Examiners heavily scrutinize delinquent tracking logs to determine whether the institution actively enforces its written compliance policy. Compliance teams must demonstrate documented evidence of managerial escalations and system access suspensions enforced against overdue staff.
-
Board of Directors Reporting and Minutes: The designated BSA compliance officer must deliver regular operational updates to the board of directors or the board audit committee. Official board meeting minutes documenting the presentation, discussion, and approval of training metrics serve as primary evidence of senior managerial oversight.
Record Retention Periods and Data Integrity
Federal regulations enforce strict recordkeeping mandates regarding compliance documentation. Under regulations governing the Bank Secrecy Act, financial institutions must maintain compliance files for a minimum of five years. However, many state supervisory authorities and internal bank risk policies enforce longer retention windows, often extending to seven years or the entire duration of an employee’s tenure plus five years. Therefore, training databases must preserve permanent data integrity.
Historical completion records, previous syllabus versions, and assessment answers must remain completely immutable. For example, if an examiner questions whether a commercial loan officer received training on trade-based money laundering prior to approving a suspicious credit line three years ago, the bank must retrieve the exact curriculum and completion certificate active on that date. Emerging platforms leverage modern credential standards to ensure data immutability, as detailed in our guide on
digital badges and Open Badges 3.0. Maintaining tamper-proof archives shields the bank from catastrophic audit findings.
Conclusion
Maintaining regulatory compliance across the commercial banking sector requires continuous diligence, executive commitment, and operational rigor. Anti-money laundering and customer due diligence mandates are not static administrative hurdles; they serve as vital operational safeguards that protect institutions from financial crime exploitation. By shifting from superficial annual reviews to comprehensive, role-tailored educational programs, banks ensure their personnel maintain sharp operational awareness across all operational lines.
Building an exam-ready compliance infrastructure demands strict adherence to statutory frequency rules, direct alignment with institutional risk assessments, and the maintenance of immutable audit evidence. When supervisory examiners arrive on site, an organized, well-documented training framework provides indisputable proof of managerial oversight and operational integrity. Ultimately, investing in a resilient compliance learning architecture safeguards your workforce, preserves your institutional reputation, and ensures the continuous safety and soundness of your banking charter.
Q1. What are the primary AML training requirements for commercial banks?
Federal banking regulations mandate that every depository institution maintain an ongoing, written AML training program. The curriculum must comprehensively cover the Bank Secrecy Act, customer identification procedures, suspicious activity reporting, currency transaction reporting, and anti-evasion measures relevant to specific employee job roles.
Q2. How often must bank employees complete AML and KYC training?
While general bank policy typically dictates an annual refresher course for all staff, federal examiners evaluate frequency based on institutional risk. High-risk operational roles, such as wire room operators and foreign correspondent specialists, often require bi-annual or quarterly updates, with immediate onboarding training required for all new hires before they access live system
Q3. What is the difference between general AML training and role-based KYC training?
General AML training introduces foundational legal principles, anti-structuring rules, and common money laundering typologies across the entire bank. Role-based KYC training specifically teaches onboarding officers, lenders, and branch managers how to verify customer identities, untangle complex corporate beneficial ownership structures, and execute Customer Due Diligence rules.
Q4. What specific training records do FFIEC examiners inspect during an audit?
Examiners review course syllabi, attendance logs with exact timestamps, comprehension assessment passing scores, materials mapped to the institutional risk assessment, board of directors training presentations, and documented escalation records for employees who missed training deadlines.
Q5. How long must banks retain BSA and AML training records?
Under federal Bank Secrecy Act regulations, institutions must retain compliance documentation for a minimum of five years. However, many financial institutions maintain training records for the duration of the employment tenure plus five to seven years to ensure defensibility during historical regulatory reviews.